

Google is preparing one of the biggest changes to the desktop operating system landscape in years.
Swif.ai is announcing preliminary MDM support for Aluminium OS, Google’s upcoming Android-based desktop operating system designed for laptops, desktops, tablets, and the next generation of Google-powered PCs.
Aluminium OS represents an unusual endpoint-management challenges and one that Swif is uniquely positioned to address.
Rather than simply being another Linux distribution or another version of ChromeOS, Aluminium brings together technologies from Android, ChromeOS, and the Linux ecosystem into a desktop operating system designed to run across traditional PC hardware.
For IT teams, that means the traditional distinction between “mobile MDM” and “desktop MDM” is becoming increasingly irrelevant.
Swif has been preparing for exactly this kind of convergence.
What Is Aluminium OS?
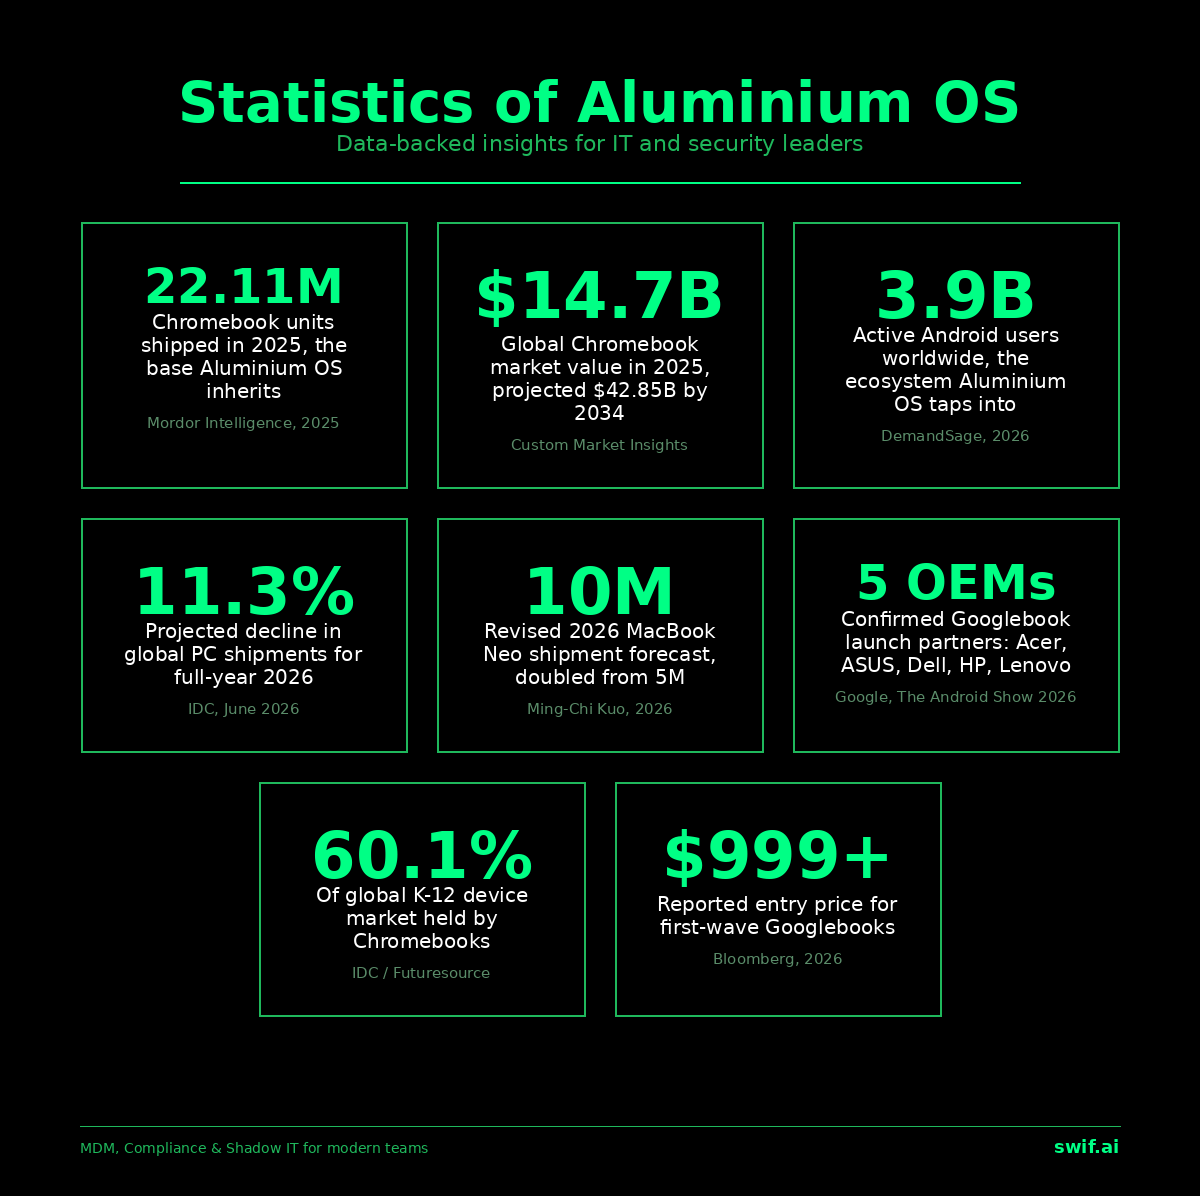
Aluminium OS is Google's upcoming desktop operating system built around Android.
Google has confirmed plans to bring Android and ChromeOS together under a unified platform, with the resulting desktop environment designed for laptops and other personal computers.
The platform uses the Linux kernel, but its operating-system family is Android and its software architecture is expected to be centered around Android technologies and APK-based applications.
Aluminium is also expected to operate across both ARM and x86 hardware, giving Android a much larger role in traditional PC environments.
This distinction is extremely important from an MDM perspective.
A computer running Aluminium may look like a traditional laptop, contain an x86 processor, have a keyboard and mouse, and be used as an employee's primary workstation.
But underneath, administrators should not assume it can be managed in exactly the same way as Ubuntu, Fedora, Debian, or another conventional Linux distribution.
That is where things get interesting.
Aluminium OS Sits Between Two MDM Worlds
Most enterprise endpoint-management platforms evolved around relatively clean operating-system boundaries.
Windows devices use Windows management frameworks.
Apple devices use Apple's MDM protocols.
Linux machines typically require an agent with access to the underlying operating system.
Android devices are generally managed through Android Enterprise, device policy controllers, managed configurations, application controls, and Android-specific security APIs.
Aluminium starts to blur those boundaries.
It brings an Android application and management model to PC-class hardware while continuing to rely on the Linux kernel underneath it.
For Swif, this isn't an entirely new problem.
We already maintain separate but complementary management architectures for Android and Linux.
Our Linux MDM currently supports distributions including Ubuntu, Debian, Fedora, Arch Linux, NixOS, OpenSUSE, RHEL, Universal Blue, and others. Linux devices can be enrolled using the Swif agent and managed for security policies, applications, OS patches, remote administration, compliance, and other endpoint functions.
At the same time, Swif's Android MDM implementation uses Android-specific management capabilities including Android Enterprise enrollment, application management, device policies, dedicated-device management, and our own Swif Mobile Security agent.
Aluminium gives us an opportunity to bring those two areas of engineering together.
Why We Aren't Treating Aluminium as "Just Linux"
One of the easiest mistakes MDM vendors could make with Aluminium is seeing "Linux kernel" and simply attempting to deploy their existing Linux agent.
The Linux kernel does not determine the complete device-management model of an operating system.
Android itself uses the Linux kernel, but managing Android is fundamentally different from managing an Ubuntu laptop.
Traditional Linux MDM agents can commonly interact with concepts such as:
- systemd services
- Linux users and groups
- package managers such as APT, DNF, Pacman, or Nix
- SSH configuration
- filesystem permissions
- desktop environments
- shell scripts
- Linux firewall implementations
- native Linux software packages
Android exposes a very different administrative surface.
Enterprise management is built around concepts such as:
- Android Enterprise
- Device Policy
- managed applications
- managed configurations
- work profiles
- fully managed devices
- dedicated devices
- application permissions
- certificate deployment
- network policies
- device security state
- Android-specific compliance signals
Aluminium may run on the same physical hardware traditionally associated with Linux PCs, but its Android foundation means many of these Android management primitives are likely to be significantly more relevant than traditional Linux configuration management.
That is why Swif's Aluminium implementation is being approached as its own endpoint class, rather than simply adding another distribution name to our Linux compatibility list.
An Android Desktop Changes What Android MDM Means
Android MDM has historically been associated primarily with smartphones, tablets, rugged devices, kiosks, scanners, and dedicated-purpose hardware.
Aluminium expands that model to something very different:
the employee's primary computer.
That introduces new expectations.
A corporate Android workstation potentially needs the same capabilities administrators expect from macOS, Windows, and Linux:
- device inventory
- identity-aware enrollment
- security posture reporting
- disk and data protection
- application inventory
- application deployment
- OS update visibility
- remote commands
- certificates
- Wi-Fi configuration
- VPN configuration
- compliance enforcement
- peripheral controls
- remote troubleshooting
- asset ownership
- device assignment
- security integrations
The endpoint might technically be Android, but the management requirements are those of a desktop computer.
That is an important architectural shift for the MDM industry.
Swif Already Maintains Native Android Management Infrastructure
Swif's Android platform is not simply a mobile inventory connector.
Swif supports Android Enterprise enrollment and Android application management, including managed Google Play applications and application deployment policies.
We also recently introduced Swif Mobile Security for Android, our dedicated Android management and security agent.
Swif Mobile Security adds another layer of endpoint visibility and allows device compliance information to remain synchronized with the Swif administrator console.
Our Android infrastructure is therefore already designed around both:
- platform-level Android management, and
- agent-assisted endpoint security and telemetry.
That combination becomes particularly important as Android moves onto general-purpose computers.
Our Linux Experience Matters Too
Aluminium's Android foundation does not make the Linux side irrelevant.
Quite the opposite.
Supporting Linux endpoints has forced Swif to design management infrastructure that works in environments where there is no single universal MDM protocol comparable to Apple's MDM framework.
Swif's Linux management architecture already handles differences in distributions, CPU architectures, package systems, desktop environments, services, security configurations, and system capabilities.
Swif currently supports Linux enrollment on both x86_64 and ARM64 for supported distributions.
That experience becomes particularly useful for Aluminium because Google intends the operating system to run across both ARM and x86 PC hardware.
The combination gives Swif two complementary management layers from which to build:
Android-native management above the operating system and Linux-aware endpoint technology closer to the underlying device.
Exactly how much of each layer Aluminium ultimately exposes to third-party management vendors will depend on Google's final enterprise APIs and production architecture.
Preliminary Support Means Preliminary
Aluminium remains an emerging platform.
For that reason, we're deliberately describing Swif's current compatibility as preliminary support.
We don't want to call an operating system fully supported before its enterprise management interfaces, production builds, enrollment workflows, security APIs, and hardware ecosystem stabilize.
During this stage, Swif is evaluating and adapting management capabilities around the areas that matter most to enterprise customers, including:
- device discovery and inventory
- enrollment
- hardware identification
- OS and build reporting
- application inventory
- Android application management
- compliance reporting
- remote management
- network configuration
- certificates
- security posture
- update management
- policy enforcement
Some capabilities may ultimately use Google's Android management interfaces.
Others may require functionality provided through Swif's endpoint agent.
And some capabilities could require new Aluminium-specific implementations.
We expect that boundary to become much clearer as Google finalizes the platform.
One Console for Android, Linux, and the New Class of Devices Between Them
This is ultimately why we built Swif as a cross-platform endpoint-management system rather than designing it around one operating system.
The definition of an endpoint keeps changing.
An ARM laptop can run Linux.
A Linux kernel can power Android.
Android can become a desktop operating system.
Applications increasingly move between mobile and desktop environments.
And organizations still need one place to answer the same fundamental questions:
What devices do we have?
Who is using them?
Are they secure?
Are they compliant?
What software is installed?
Can IT remotely manage them?
Aluminium OS is a particularly good example of why endpoint management needs to move beyond the traditional Windows/macOS/mobile categories.
Preparing for the Next Generation of Android PCs
Google's move toward an Android-powered desktop platform could significantly expand the kinds of devices enterprise IT teams classify as Android endpoints.
Instead of managing Android phones alongside employee laptops, IT organizations may soon be managing Android phones and Android laptops as parts of the same fleet.
Swif intends to make that transition as straightforward as possible.
Our existing investments in Android Enterprise management, Swif Mobile Security, Linux MDM, ARM64 support, x86_64 support, application management, compliance automation, and remote endpoint administration give us a strong technical foundation for this new category of device.
Preliminary Aluminium OS support is the first step.
As Google continues to finalize the platform, Swif will continue expanding compatibility and documenting which policies and management capabilities are available for production deployments.
If your organization is already testing Aluminium OS or evaluating Android-powered PCs for enterprise use, we'd love to hear about your environment and the management capabilities you need.
Swif.ai is building MDM for what comes after the traditional desktop operating system.