

SOC 2 Attested • GDPR • EU Data Residency • Free for 5
CORE CAPABILITIES
Vulnerabilities, misconfigurations & active threats, found in real time.
Risks ranked automatically, no manual triage needed.

Findings mapped to SOC 2, ISO 27001 & HIPAA.
Security data feeds straight into your Swif dashboard.
OUTCOMES
top risks surfaced, not a flood of raw alerts
vulnerabilities found and actioned quicker
findings mapped to compliance, less prep work
BUILT FOR REAL TEAMS
SECURITY, PRIVACY & TRUST
Manage devices & policy, full audit trail included.

Traffic encrypted in transit & at rest, BYOD data separated.
SOC 2, ISO 27001 & HIPAA, dashboards with exportable evidence.

“Swif.ai has effectively solved our software deployment and unified device management challenges. Their customer support is equally impressive — issues are resolved quickly and efficiently.”

Hanson Han
Head of Platform Engineering at OpusClip
FAQ
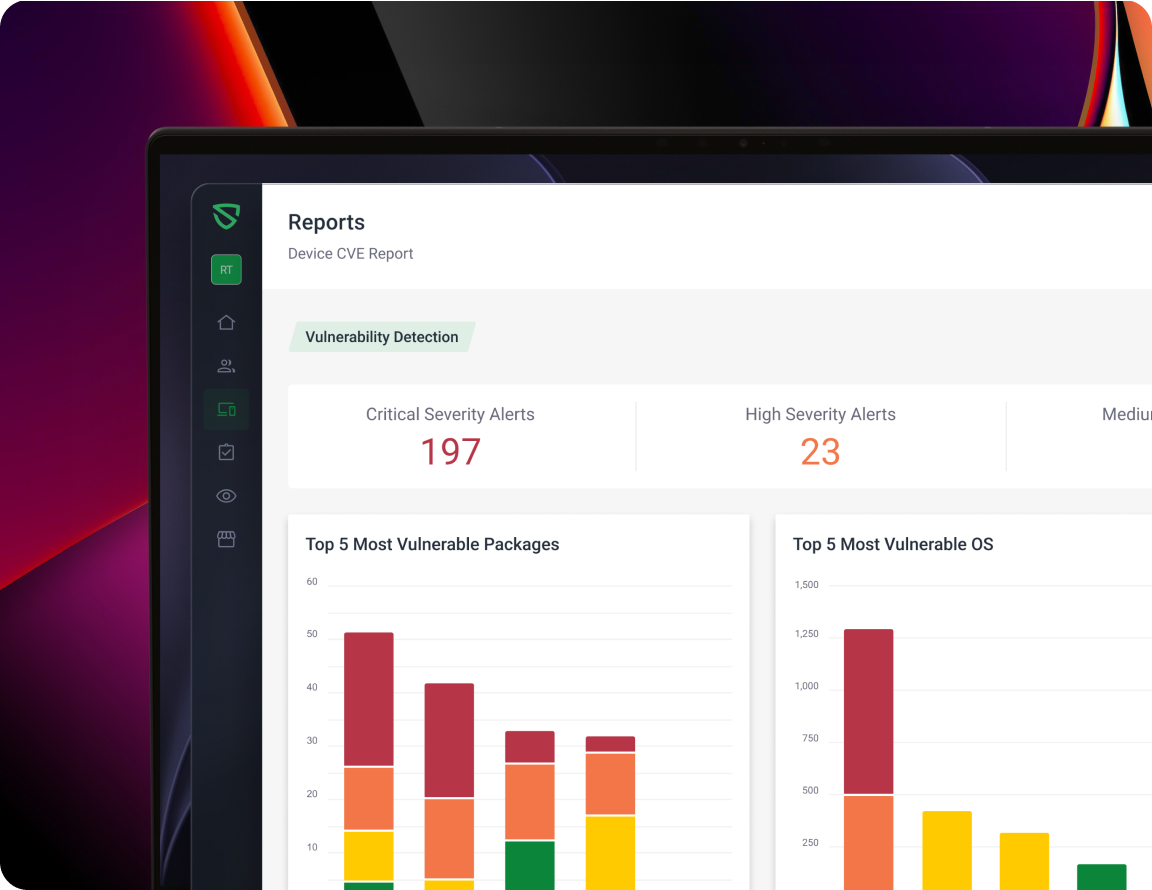
A vulnerability report built on the Wazuh engine, showing known CVEs, risky packages and vulnerable OS versions across your fleet.
By severity, critical, high, medium or low, so you can act on what matters before what doesn't.
Turn on the CVE Logger Policy for each platform. Data collection and reporting start automatically from there.
Yes. Findings map to frameworks like SOC 2, ISO 27001 and HIPAA, so reports are ready to share with auditors.
The CVE Report makes enterprise security simple, smart and audit ready.